
Penetration Testing That Protects Your Business
CISSP and OSCP-certified testers find what scanners miss, with reports accepted by SOC 2, ISO 27001 and PCI-DSS auditors.
Featured Security Assessments
Results from recent engagements
Penetration Testing Services
Manual, expert-led testing for every attack surface you ship
Web Application
Business logic flaws, auth bypasses and privilege escalation that DAST tools miss, manually validated and CVSS-scored.
Mobile Application
iOS & Android binary analysis, insecure data storage, certificate pinning bypass and inter-app flaws.
API Testing
REST, GraphQL & SOAP tested for BOLA, mass assignment and the OWASP API Top 10.
Network Infrastructure
External perimeter, internal lateral movement, firewall rules and network segmentation.
Cloud Security
AWS, Azure & GCP review: IAM escalation, public buckets, open security groups, metadata exposure.
Kubernetes
RBAC misconfigurations, pod-to-pod lateral movement, privileged containers and etcd access control.
LLM / AI Security
Prompt injection, indirect injection via RAG pipelines, training data extraction and system-prompt jailbreaks.
Process & Deliverables
OWASP & PTES-aligned, from kickoff to verified fix
Scoping & Setup
Day 1Scope documented and environment configured so testing starts fast.
Recon & Exploitation
1-2 WeeksAttack surface mapping, then manual exploitation to validate every finding.
Reporting
1-2 DaysFindings delivered as the three documents below.
Remediation Support
OngoingExpert guidance during fixes, plus a free re-test.
Technical Finding Report
Proof-of-concept, CVSS scoring and step-by-step remediation for your engineers.
Executive Summary Report
Business impact and risk overview for leadership.
Letter of Attestation
Proof of testing for auditors, enterprise clients and regulators.
Community & Events
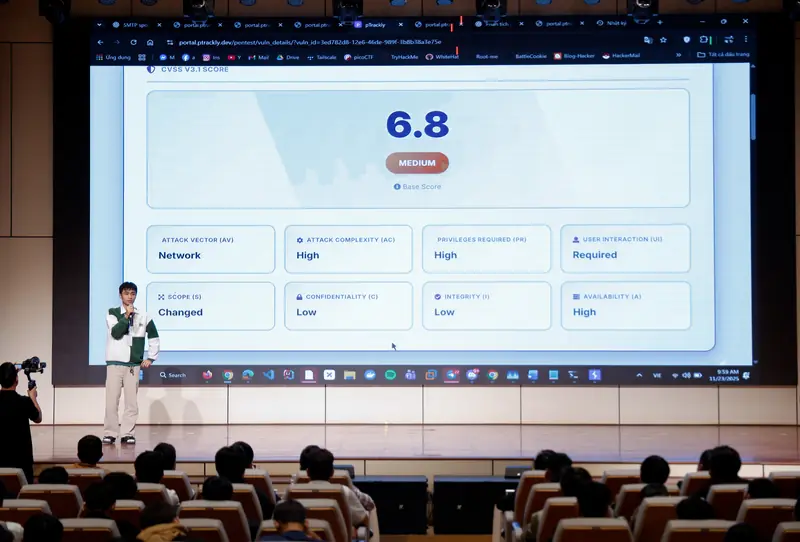
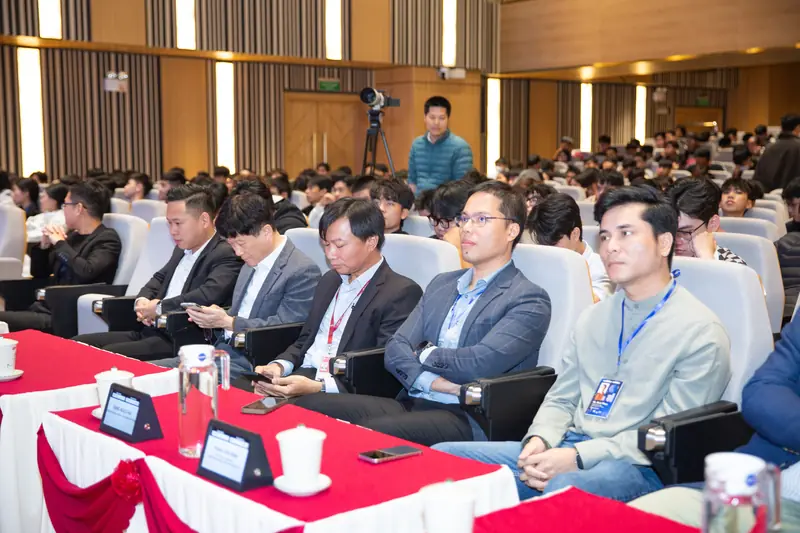
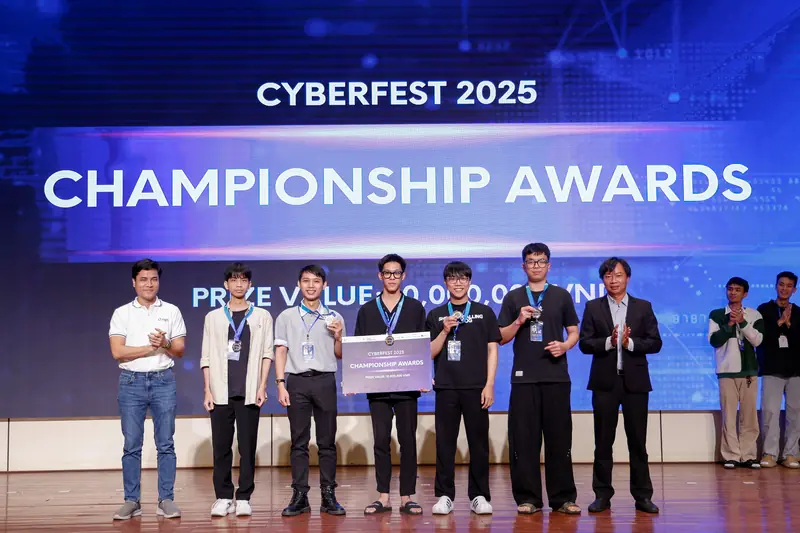
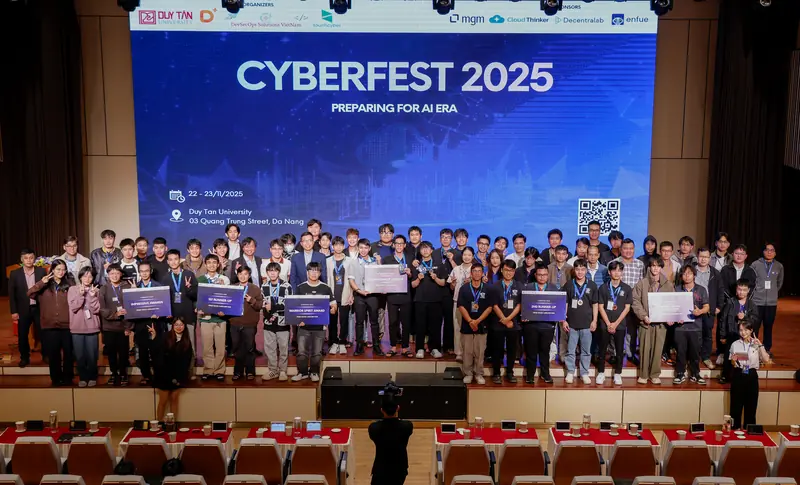
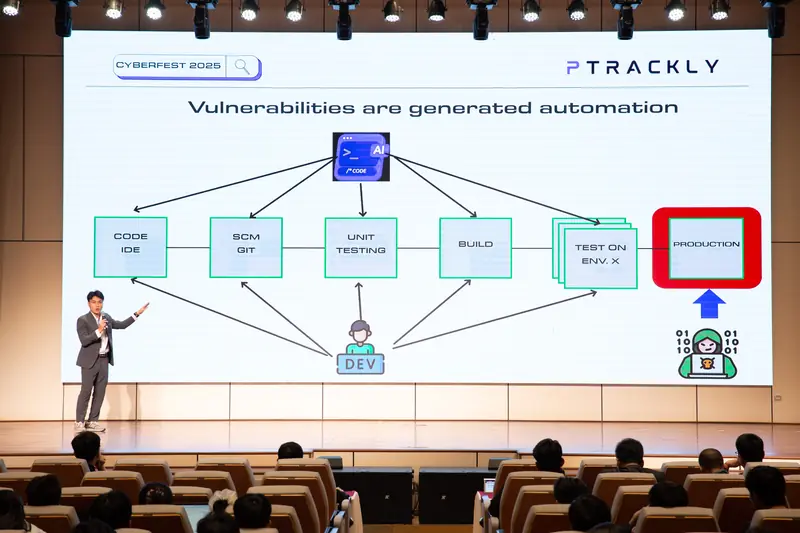
Bug bounties, conference talks, open-source tools and hands-on workshops across Southeast Asia
Penetration Testing FAQ
Scope, cost, timelines and compliance
Most pentests take 1-2 weeks. A focused web app test takes 5-7 business days; multi-system assessments take 2-3 weeks. Critical findings are shared within the first few days so remediation can start immediately.
Yes. Reports are accepted by auditors for SOC 2, ISO 27001, PCI-DSS and HIPAA, with evidence mapped to the control requirements.
Cost depends on scope, complexity, testing method and number of targets. Request a scoped quote so the estimate matches the systems actually tested.
A vulnerability scan is automated: fast, but full of false positives and blind to business logic. A penetration test is manual: experts chain vulnerabilities and validate exploitability, finding auth bypasses and privilege escalation that scanners miss.
VAPT (Vulnerability Assessment and Penetration Testing) combines breadth (systematic vulnerability assessment) with depth (manual exploitation). Our engagements cover both, and every finding includes exploitation evidence.
Yes, across Vietnam, Singapore and Southeast Asia. Most testing is remote, with on-site options for internal network and physical assessments. Reports meet MAS and Vietnam Law on Cybersecurity requirements.
Ready to Secure Your Infrastructure?
Get a pentest quote or talk to a security engineer